Use the evidence and practical questions in this article to test your own assumptions. Any worked examples use hypothetical inputs.
The difference that matters at sign-in
A password is a secret a person enters and a service checks. A passkey uses a cryptographic credential tied to the service, with a device or credential provider helping the user authenticate. FIDO’s guidance explains why passkeys can resist ordinary credential phishing: a convincing imitation site cannot simply collect a reusable password from that sign-in. That does not remove every account risk. Recovery channels, compromised devices and weak administrative controls still matter. For a US business, treat adoption as an identity project, beginning with the email and administrator accounts that control access to other systems.
Pilot the recovery path before wide enrollment
Choose a small group with different devices and ordinary working conditions. Test enrollment, a new-device login and the loss of the normal device. Find out whether credentials sync through an approved company-managed service or depend on a personal account. Document what happens when an employee leaves and who can revoke access. Give administrators a controlled recovery method that does not rely on one person’s phone. A security key may be useful where the service and organizational policy support it, but procurement must include spare access and a secure storage arrangement.
A rollout checklist with a stopping condition
Do not disable every old sign-in route before the pilot proves that real staff can recover their accounts. Identify services that do not support the proposed method and give those exceptions a review date. Track successful enrollment, recovery failures and support time. If users routinely bypass the new method, investigate the workflow before calling the rollout complete. Keep clear instructions for reporting an unexpected sign-in prompt. The objective is stronger authentication that the business can operate reliably, not a technology label applied while an insecure recovery channel remains unchanged. Review the setup after device changes and staff departures.
- Inventory supported services, account owners and approved devices.
- Test lost-device recovery and administrator access.
- Retire weaker routes only after a controlled successful pilot.
Image source and usage
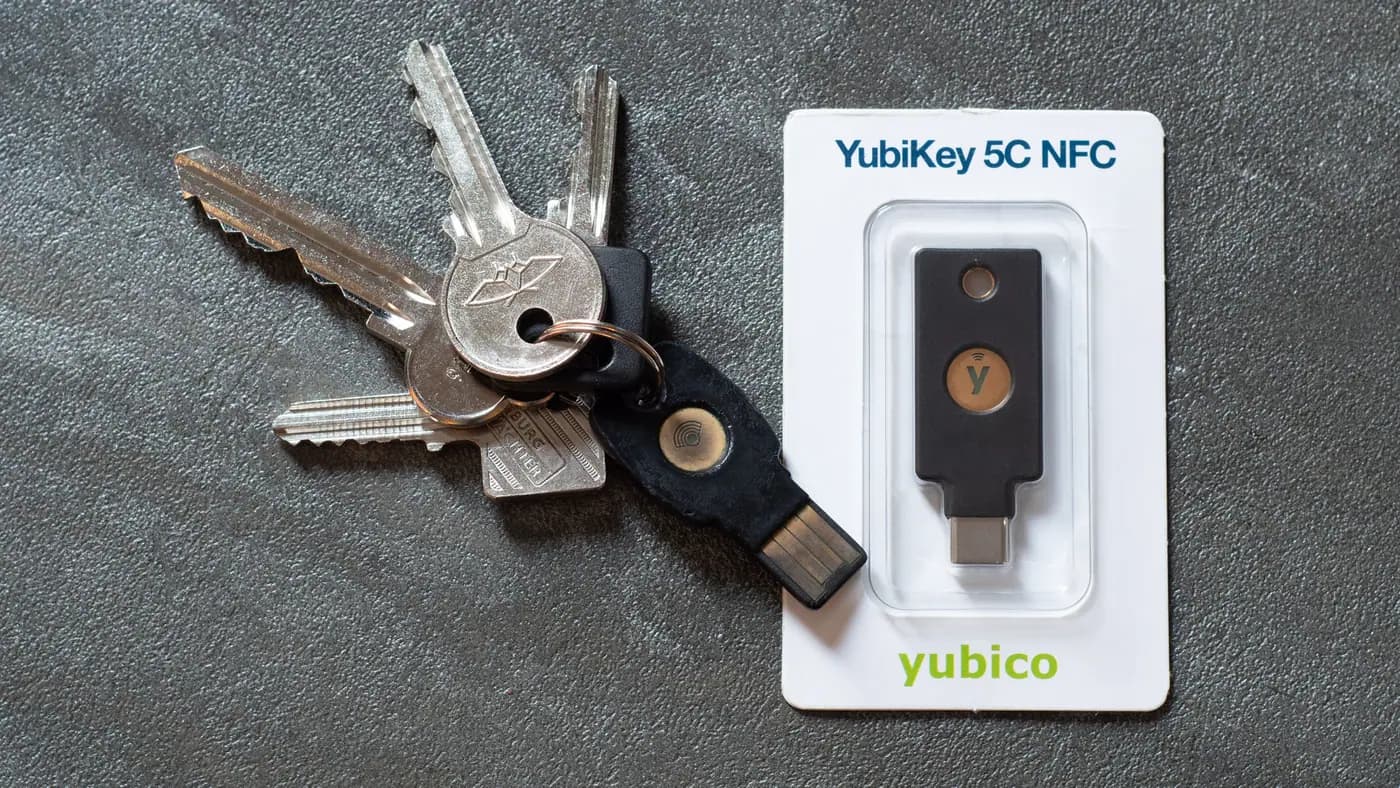
A YubiKey 5C NFC security key, shown as an authentication reference
Daniel Aleksandersen
Source image · Image-use terms
Web versions are resized and compressed; attribution and applicable source terms are retained.
Frequently asked questions
Are passkeys identical to biometric data?
No. A device may use a biometric check to unlock a credential, but the passkey is a cryptographic sign-in mechanism.
Can a business ignore account recovery after adopting passkeys?
No. Recovery and administrative access need deliberate controls and testing.
Sources & further reading
Source links checked October 20, 2026. Rules and availability may change; verify current terms directly. Read our editorial standards.