Use the evidence and practical questions in this article to test your own assumptions. Any worked examples use hypothetical inputs.
Prepare decisions before an incident
A data breach response plan should identify who can authorize containment, engage specialists and communicate with affected people. FTC guidance provides a starting point, but notification duties depend on the facts, data, locations and applicable rules. Do not assume one deadline covers every US business. Keep verified contact information for the administrator, legal adviser, insurer and relevant service providers outside the system most likely to be unavailable. Give each contact a role rather than leaving an unstructured phone list. Review the plan when the business begins collecting a new kind of sensitive information.
Preserve evidence while containing harm
If an incident is suspected, record what was observed, when and by whom. Notify the approved response lead and avoid improvised deletion, reinstallation or public speculation. A specialist should guide isolation and preservation so that containment does not destroy useful evidence. Track affected accounts and systems in a controlled incident log. Separate confirmed facts from possibilities and identify what remains unknown. If a vendor is involved, obtain a responsible contact and preserve its communications. Continue essential work only through approved alternatives that do not copy exposed data into another unmanaged environment.
Review the insurance policy’s incident-reporting instructions before engaging outside support. Record the approved contacts and any required coordination. A preparation exercise should verify those routes without submitting a fictional claim or contacting outside organizations as if an incident occurred.
Review notification and recovery separately
Restoring a service does not establish that the incident is over or determine whether notification is required. Work with qualified advisers to assess the affected information and applicable obligations. Prepare communications that describe verified facts and useful actions without promising facts the investigation has not established. Record the approval of each external statement. After recovery, test the corrective measures and update access, vendor and retention practices where needed. A tabletop exercise can rehearse these decisions using a fictional incident before a real emergency occurs. The outcome should be a clear chain of responsibility and evidence, not a claim that the business can guarantee prevention.
- Keep verified response contacts and authority outside the affected system.
- Document facts and preserve evidence under specialist guidance.
- Review notification duties, communications and restoration as separate workstreams.
Image source and usage
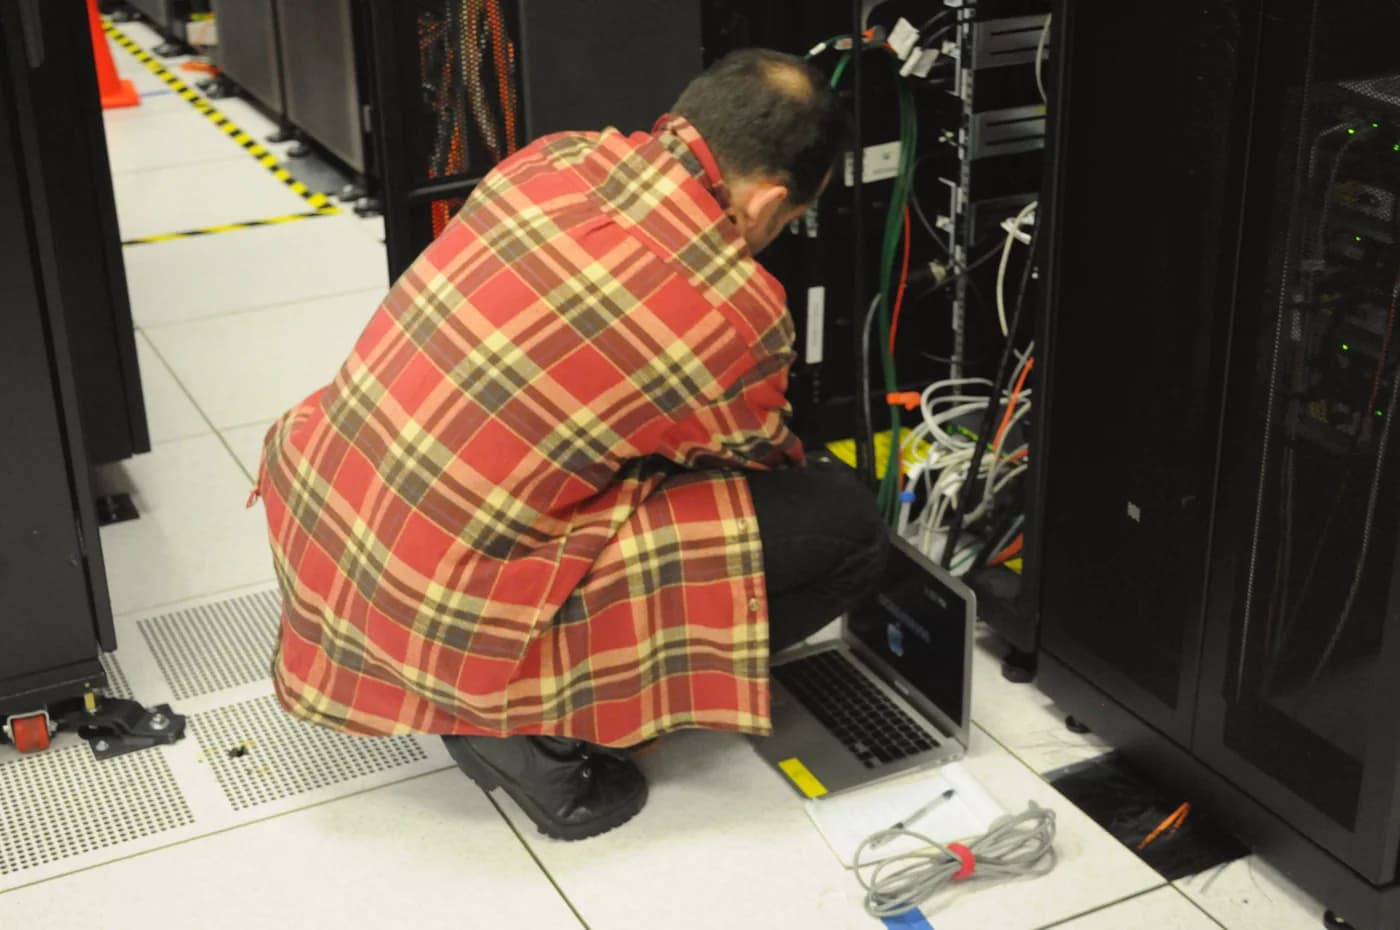
A technician using a laptop beside server racks at NERSC
Derrick Coetzee from Berkeley, CA, USA
Source image · Image-use terms
Web versions are resized and compressed; attribution and applicable source terms are retained.
Frequently asked questions
Does restoring a system remove notification duties?
No. Notification depends on the incident facts and applicable rules, not only service availability.
Should staff erase suspected compromised devices immediately?
Avoid improvised erasure; seek specialist containment and evidence-preservation guidance.
Sources & further reading
- Data Breach Response: A Guide for Business | Federal Trade Commission
- Small Business Cybersecurity Corner | NIST
Source links checked October 20, 2026. Rules and availability may change; verify current terms directly. Read our editorial standards.