Use the evidence and practical questions in this article to test your own assumptions. Any worked examples use hypothetical inputs.
Three mechanisms with different jobs
SPF identifies systems authorized to send for a domain, DKIM attaches a verifiable signature to a message and DMARC connects authentication with the visible From domain through alignment. They are related controls, not interchangeable settings. CISA’s email-security directive and Google’s administrator documentation explain these mechanisms in their respective contexts. For a US business, the practical task starts with discovering every legitimate sender. A marketing platform, invoicing application, support desk and ordinary mailbox provider can all send on the company’s behalf. A rushed policy change can therefore disrupt real customer communication.
Inventory senders before proposing DNS changes
Create a sender register with service owner, purpose, sending domain and a sample message. Ask the mail administrator to inspect authentication results and current DNS records. Preserve the existing zone and distinguish website records from mail-related records. Do not add a second conflicting SPF record or copy an example policy without understanding current services. Establish how reports will be received and reviewed. Forwarding, third-party services and multiple domains can complicate alignment, so the review should include actual customer-facing messages rather than a single test from the main mailbox.
Record a baseline of representative successful messages before proposing changes. It gives the administrator a comparison if a service later fails. Keep the sender owner involved so a technically correct policy is checked against real business delivery.
Use a staged verification and rollback plan
A written proposal should identify the intended policy, affected senders, verification method and rollback record. Review reports and test legitimate services before moving to a stricter policy. Ask a recipient outside the company to confirm that representative messages arrive and inspect their authentication results where available. Successful DNS publication alone does not prove delivery. Keep monitoring after changes because new software may introduce another sender. This article provides a planning framework only; it does not change DNS or assert that a company’s existing email setup is incorrect. The goal is authenticated delivery without silently breaking an essential business workflow.
- List all legitimate senders and preserve current records.
- Check alignment on real messages from each service.
- Stage changes, confirm delivery and keep a rollback.
Image source and usage
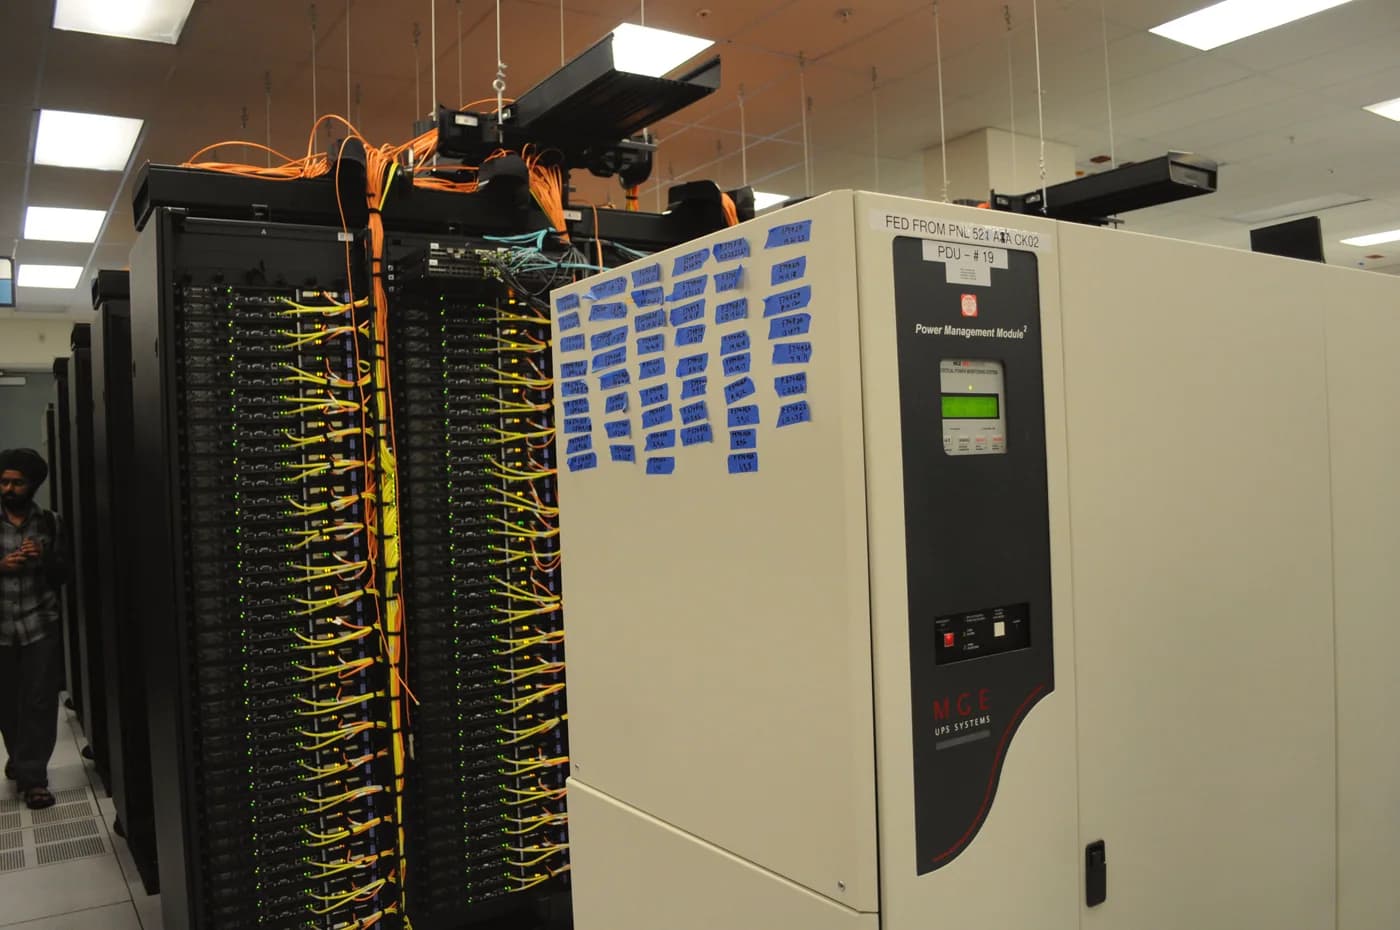
Server racks and network cabling at the NERSC data center
Derrick Coetzee from Berkeley, CA, USA
Source image · Image-use terms
Web versions are resized and compressed; attribution and applicable source terms are retained.
Frequently asked questions
Does SPF alone authenticate the visible From address?
Not necessarily. DMARC alignment connects authentication results with the visible From domain.
Does publishing DNS prove email was delivered?
No. Verify authentication and actual receipt for each legitimate sending service.
Sources & further reading
- BOD 18-01: Enhance Email and Web Security | CISA
- DMARC সেট আপ করুন | Security & data protection | Google Workspace Help
Source links checked October 20, 2026. Rules and availability may change; verify current terms directly. Read our editorial standards.