Use the evidence and practical questions in this article to test your own assumptions. Any worked examples use hypothetical inputs.
Review access against a real job need
A user access review asks whether each person still needs each permission for their current responsibilities. Start with business-critical systems such as email, banking administration, payroll, cloud files and customer tools. Identify a business owner who can judge the need, not just an IT operator who can remove an account. A person being employed does not mean every old project permission remains appropriate. Likewise, a contractor’s ongoing relationship does not justify indefinite access to unrelated client folders or administrator controls.
Include accounts that are easy to miss
Export or review users, roles, groups, service accounts, API credentials, external guests and public sharing links through approved administrative tools. Keep credential values out of the review spreadsheet. Ask who owns each integration and whether a former employee remains its only recovery contact. For a hypothetical agency, a disabled email account does not necessarily revoke access to a separately hosted design or advertising platform. Review connected applications and active sessions using the vendor’s supported controls.
Approve changes without breaking the business
Classify each permission as retain, reduce, remove or investigate. Require an owner and reason for privileged access. Before disabling a service identity, confirm dependencies, transfer ownership and prepare a tested replacement where needed. Do not delete customer records or shared files merely to remove a former user’s login. Follow the system’s account-disable and ownership-transfer process. Escalate uncertain access promptly rather than leaving an unowned administrator active because the team is afraid of an undocumented dependency.
Verify the result and repeat on triggers
Record the approved change, completion date and evidence that the permission actually changed. Verify a removed guest no longer sees the shared resource and a reduced user no longer has administrator actions, using safe checks. Trigger reviews after departures, role changes, contract completion and major system changes, with a regular review cadence as well. MFA helps protect sign-in but does not make excessive permissions appropriate. A completed review is a verified access state, not just a circulated spreadsheet with every row marked approved.
Check recovery and ownership contacts
Review account recovery emails, administrator backups and integration ownership after changing permissions. A former user can remain a recovery contact even when the visible business role has changed. Follow the vendor’s supported transfer process and verify the new authorized owner can administer the account without relying on the departed person.
Image source and usage
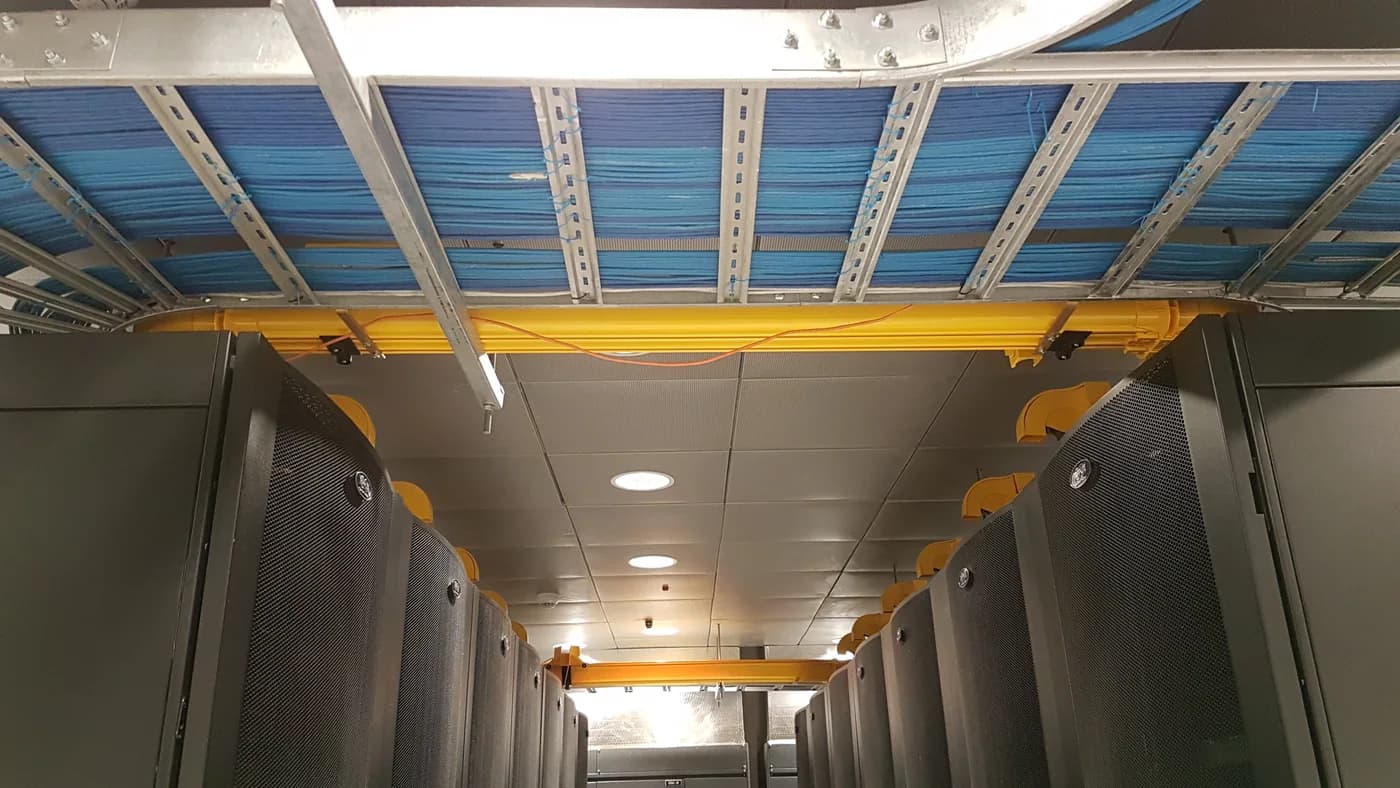
Installation work in the Summit computer room
Rubin Observatory/NSF/AURA
Source image · Image-use terms
Web versions are resized and compressed; attribution and applicable source terms are retained.
Frequently asked questions
Does MFA replace access reviews?
No. Authentication and authorization address different questions.
Should I delete files to remove a user?
No. Review account disabling and ownership transfer without destroying required records.
Sources & further reading
Source links checked October 23, 2026. Rules and availability may change; verify current terms directly. Read our editorial standards.